BBC - 3 November 2010

Information Commissioner, Christopher Graham: "I think the important thing was to get the foot in the door for an audit of Google which had to be by consent"
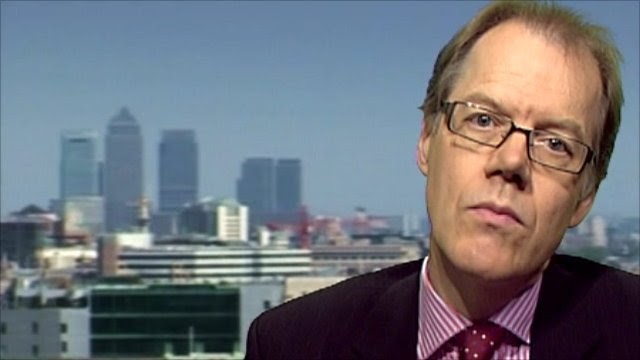
Information Commissioner, Christopher Graham: "I think the important thing was to get the foot in the door for an audit of Google which had to be by consent"
There was a "significant breach" of the Data Protection Act when Google collected personal data via its Street View cars, the UK's Information Commissioner has ruled.
But Google will not face a fine or any punishment, Christopher Graham added.
Instead, the Information Commissioner's Office (ICO) will audit Google's data protection practices.
The move marks a U-turn for the ICO which originally ruled that no data breach had occurred.
Last week the ICO vowed to look again at the evidence, after the Canadian data agency found the search giant in breach of its law.
Its decision was welcomed by MP Robert Halfon, who has been critical of the ICO and of Google, which he recently accused of deliberately collecting the data for commercial gain.
However, he said that action had come too late.
"The ICO failed to act when it should have done, despite the fact that Google staged a significant infringement of privacy and civil liberties, by harvesting millions of e-mails, wi-fi addresses, and passwords.
"Furthermore, the ICO has already proved that it lacks the technical expertise to audit Google's activity. What confidence can we have in their audit now? People feel powerless."
The ICO said it "strongly refutes" Mr Halfon's suggestion that it did not have "the necessary expertise to audit" Google.
"We have a team of experienced and qualified auditors who regularly check organisations compliance with data protection requirements."
Mr Graham said Google must delete the data - collected from unsecured wi-fi networks - "as soon as it is legally cleared to do so".
Google has apologised for collecting the data, which it said had been done by mistake.
'Profoundly sorry'
Google has been the subject of scrutiny from data protection agencies around the world, following news that software in its Street View cars collected personal information.

Street View has been under scrutiny in Germany
This was revealed following a request from the German data commissioner to audit all the data being collected by Street View cars.
Google discovered that, along with legitimate data about the location of wi-fi hotspots, the cars were also hoovering up personal details from unsecured networks, known as payload data.
Peter Fleischer, Google's Global Privacy Counsel, said the firm was "profoundly sorry for mistakenly collecting payload data in the UK".
Google said it happened as the result of code written by one of its engineers being mistakenly incorporated in the Street View software.
"Since we announced our mistake in May we have co-operated closely with the ICO and worked to improve our internal controls," said Mr Fleischer.
"We are in the process of confirming that there are no outstanding legal obligations upon us to retain the data, and will then ensure that it is quickly and safely deleted."
'Serious violation'
It announced recently that it would appoint a head of privacy and ensure that all its engineering teams followed strict privacy protocols.
New impetus was given to the UK enquiry, which had originally ruled that no significant breach had occurred, following harsh criticisms of Google from the Canadian authorities.
Last month it found that the search giant had breached its privacy laws.
"This incident was a serious violation of Canadian's privacy rights," privacy commissioner Jennifer Stoddart concluded.
But she said that no further action would be taken if Google tightened its privacy policies.
Backlash
Street View is now available in around 20 countries and allows uses to walk through towns and cities using photos taken by the Street View cars.
Anyone wishing to have an image removed can request this from Google.
But there is a growing backlash against the service, following complaints from people that their privacy was breached when the photos were taken.
In Germany, where Google is imminently rolling out a service, the government forced it to allow people to opt out of the service before pictures went live.
Italy has asked it to give citizens notice before starting mapping operations while the Czech Republic has banned it from taking any more pictures.


